Product

Security & Governance

Close the gaps before the breach.

A single security surface across your cloud, clusters, containers and servers — mapped to the regulations and standards that apply to you, with evidence packs ready for the auditor.

The Friday night heist

A Kenyan financial institution lost KES 1.59 billion in a single night. An unmonitored API was exploited after hours. No real-time alerting. No automatic block. The breach ran for hours before anyone noticed.

Central Bank of Kenya cybercrime data · 2024

KES 1.59B
stolen overnight in Kenya — 2024
What it does
  • Scans infrastructure continuously for misconfigurations
  • Detects exposed credentials, open ports and missing MFA
  • Maps findings to ISO 27001, PCI-DSS and central-bank rules
  • Generates compliance documentation automatically
What it finds
  • Misconfigured storage buckets and publicly exposed data
  • IAM policies with excessive or wildcard permissions
  • API keys and credentials committed to code
  • Open security groups and unprotected management ports
  • Missing MFA on privileged accounts
Who it's for
  • SACCOs and MFIs under central-bank or data regulator oversight
  • Fintechs preparing for compliance audit or investor review
  • Healthtechs handling patient data
  • Engineering teams without a dedicated security role
Real cases

Then — and with Pneuma.

Three real incidents, how they played out, and how Pneuma would have shortened them.

Case 01Kenya · April 2024

A week of fraudulent payouts, found after the money left

KES 179.6m
paid out in a week; reports put losses at up to $2.1m

TechCabal, 17 & 24 April 2024; Techpoint Africa, 25 April 2024

Then

A week — spotted only once the funds had moved

With Pneuma

Day one — the platform flags any program a server has never run, or one that differs from the same file on other servers. Fingerprint checked against threat intel; process killed or server isolated with every action recorded.

Case 02Uganda · October 2020

A payment aggregator breached; mobile money halted

$3.2m+
estimated stolen through a payment aggregator

Quartz, 7 October 2020; CommsRisk, October 2020

Then

About 3 days — undetected while transfers were abused

With Pneuma

Minutes to detect — a shell started by a web server or a known-bad connection raises a critical alert. On-call paged; server isolated or address blocked within an hour.

Case 03United States · 2018

An unlocked Kubernetes console ran a crypto miner

Cloud keys
exposed in a pod; hidden crypto miner ran unnoticed

BleepingComputer, 20 February 2018

Then

Discovered by an outside researcher — not the owner

With Pneuma

First scan flags clusters against NSA, MITRE and CIS controls. Unsafe pods refused at admission. A cryptocurrency miner — even renamed — raises a critical detection; workload isolated with a second approver.

Inside the product

See it, before you commit.

Real screens from Pneuma — the platform behind every SpectraNode product. Deploy it in your environment during the free trial.

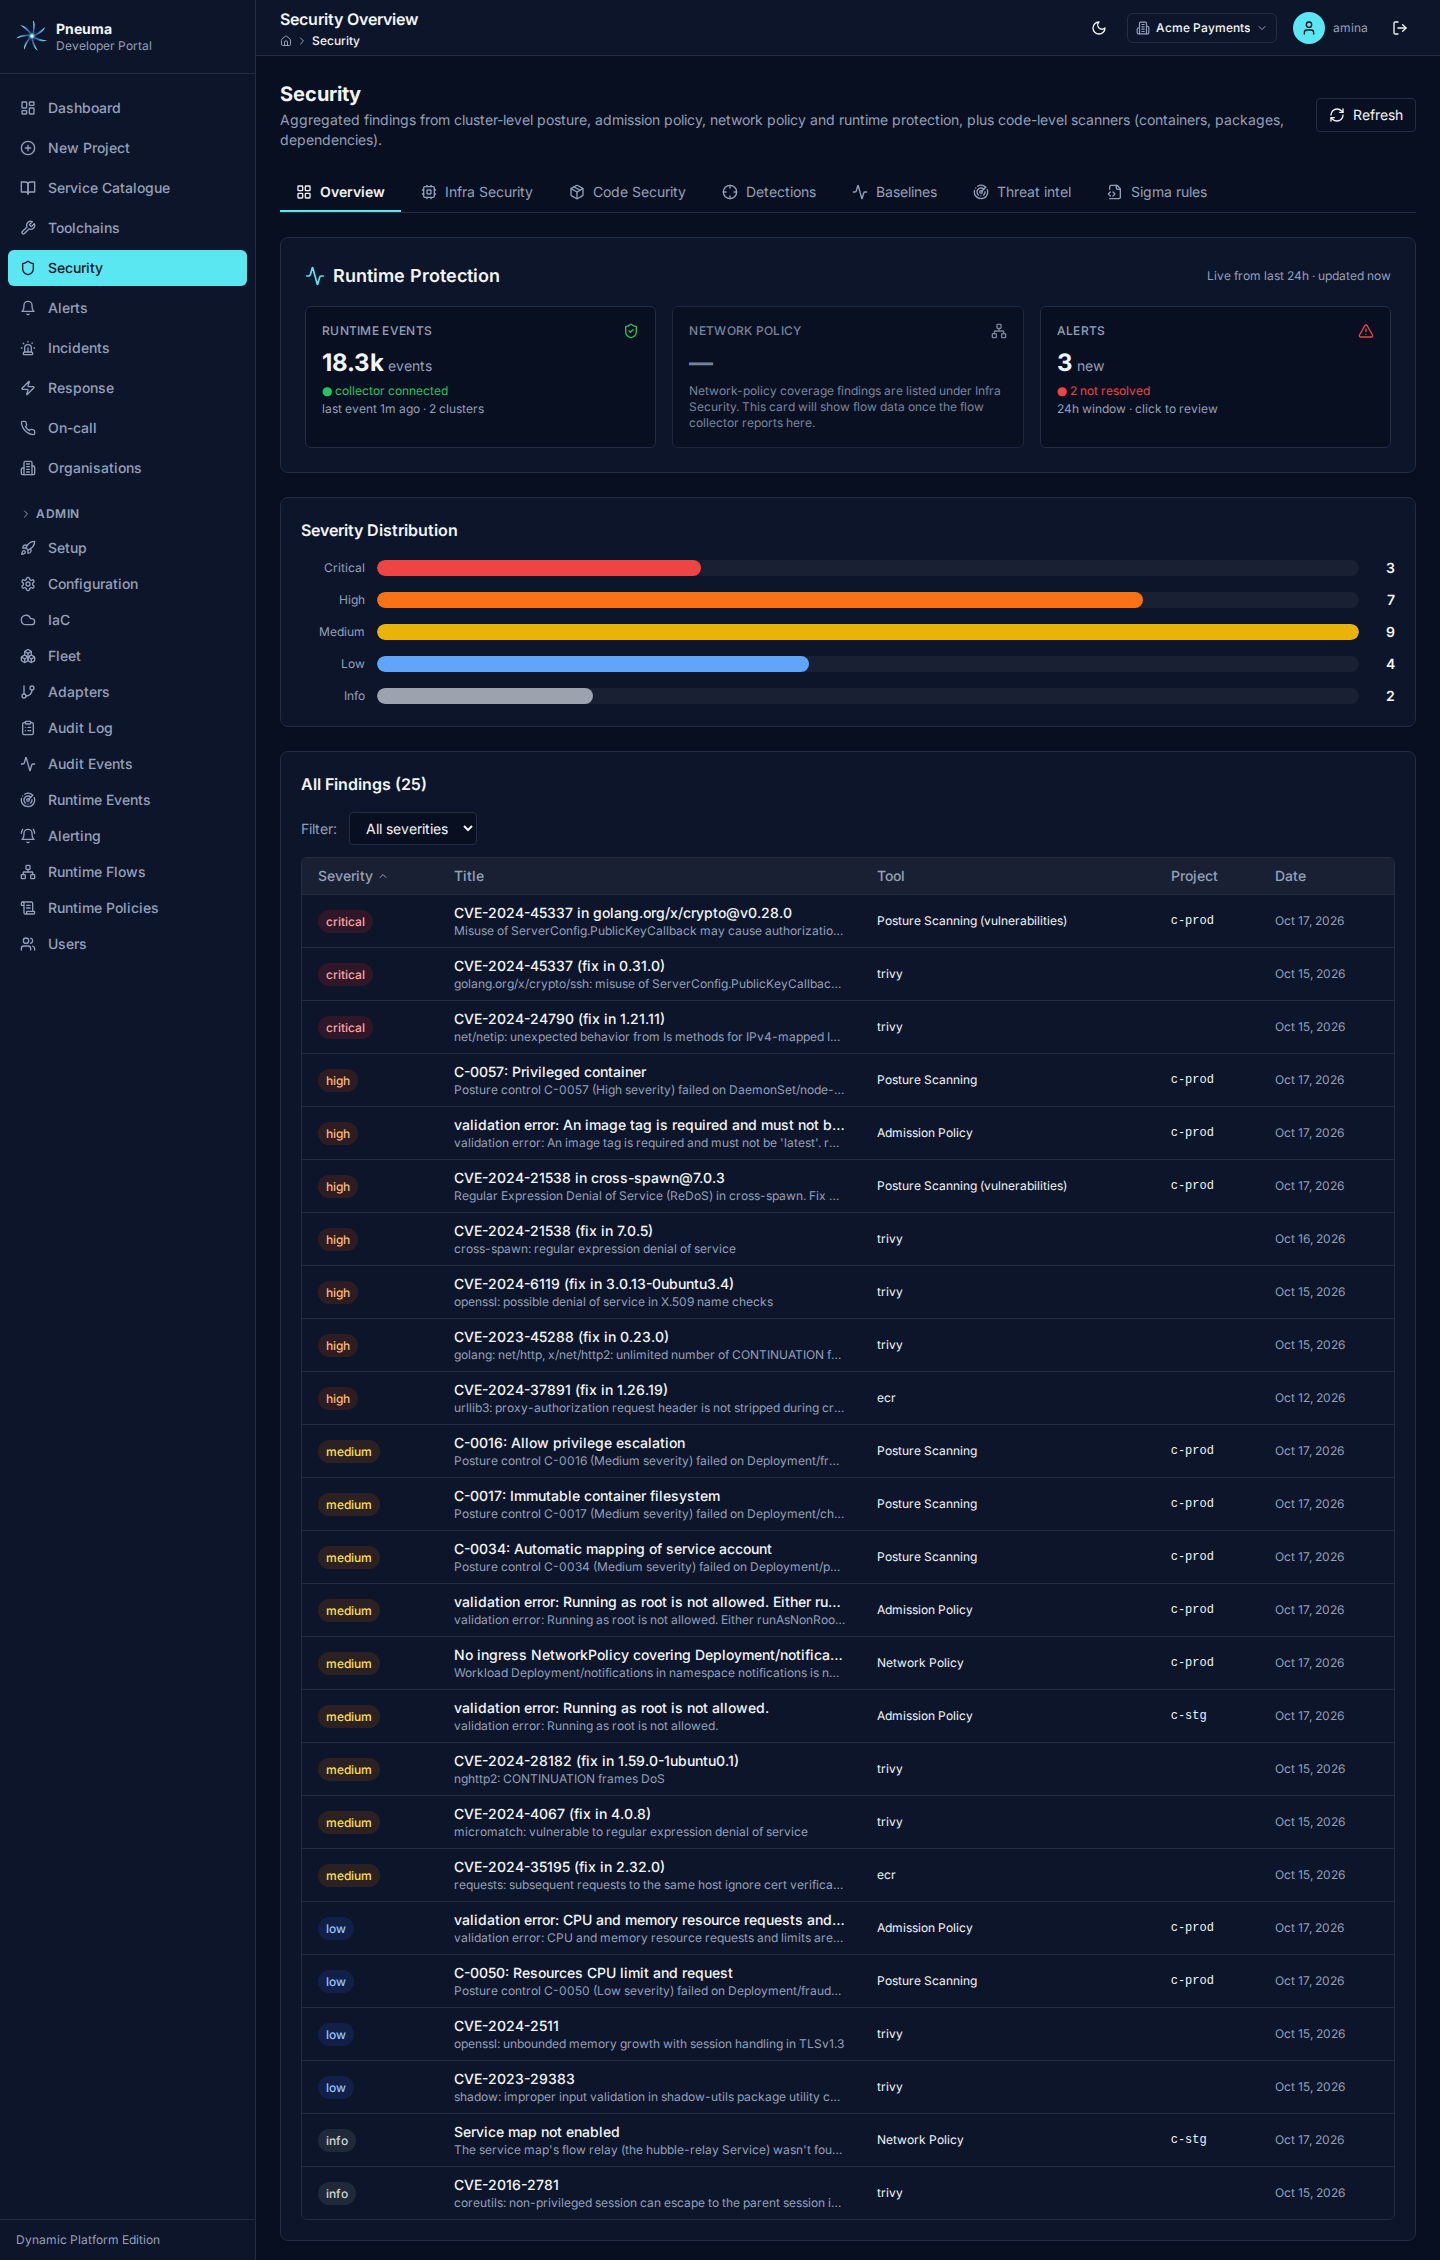
Pneuma Security Overview dashboard — severity distribution, runtime protection stats and 25 findings across posture, admission and runtime scanners.
Every finding, every severity, in one place.
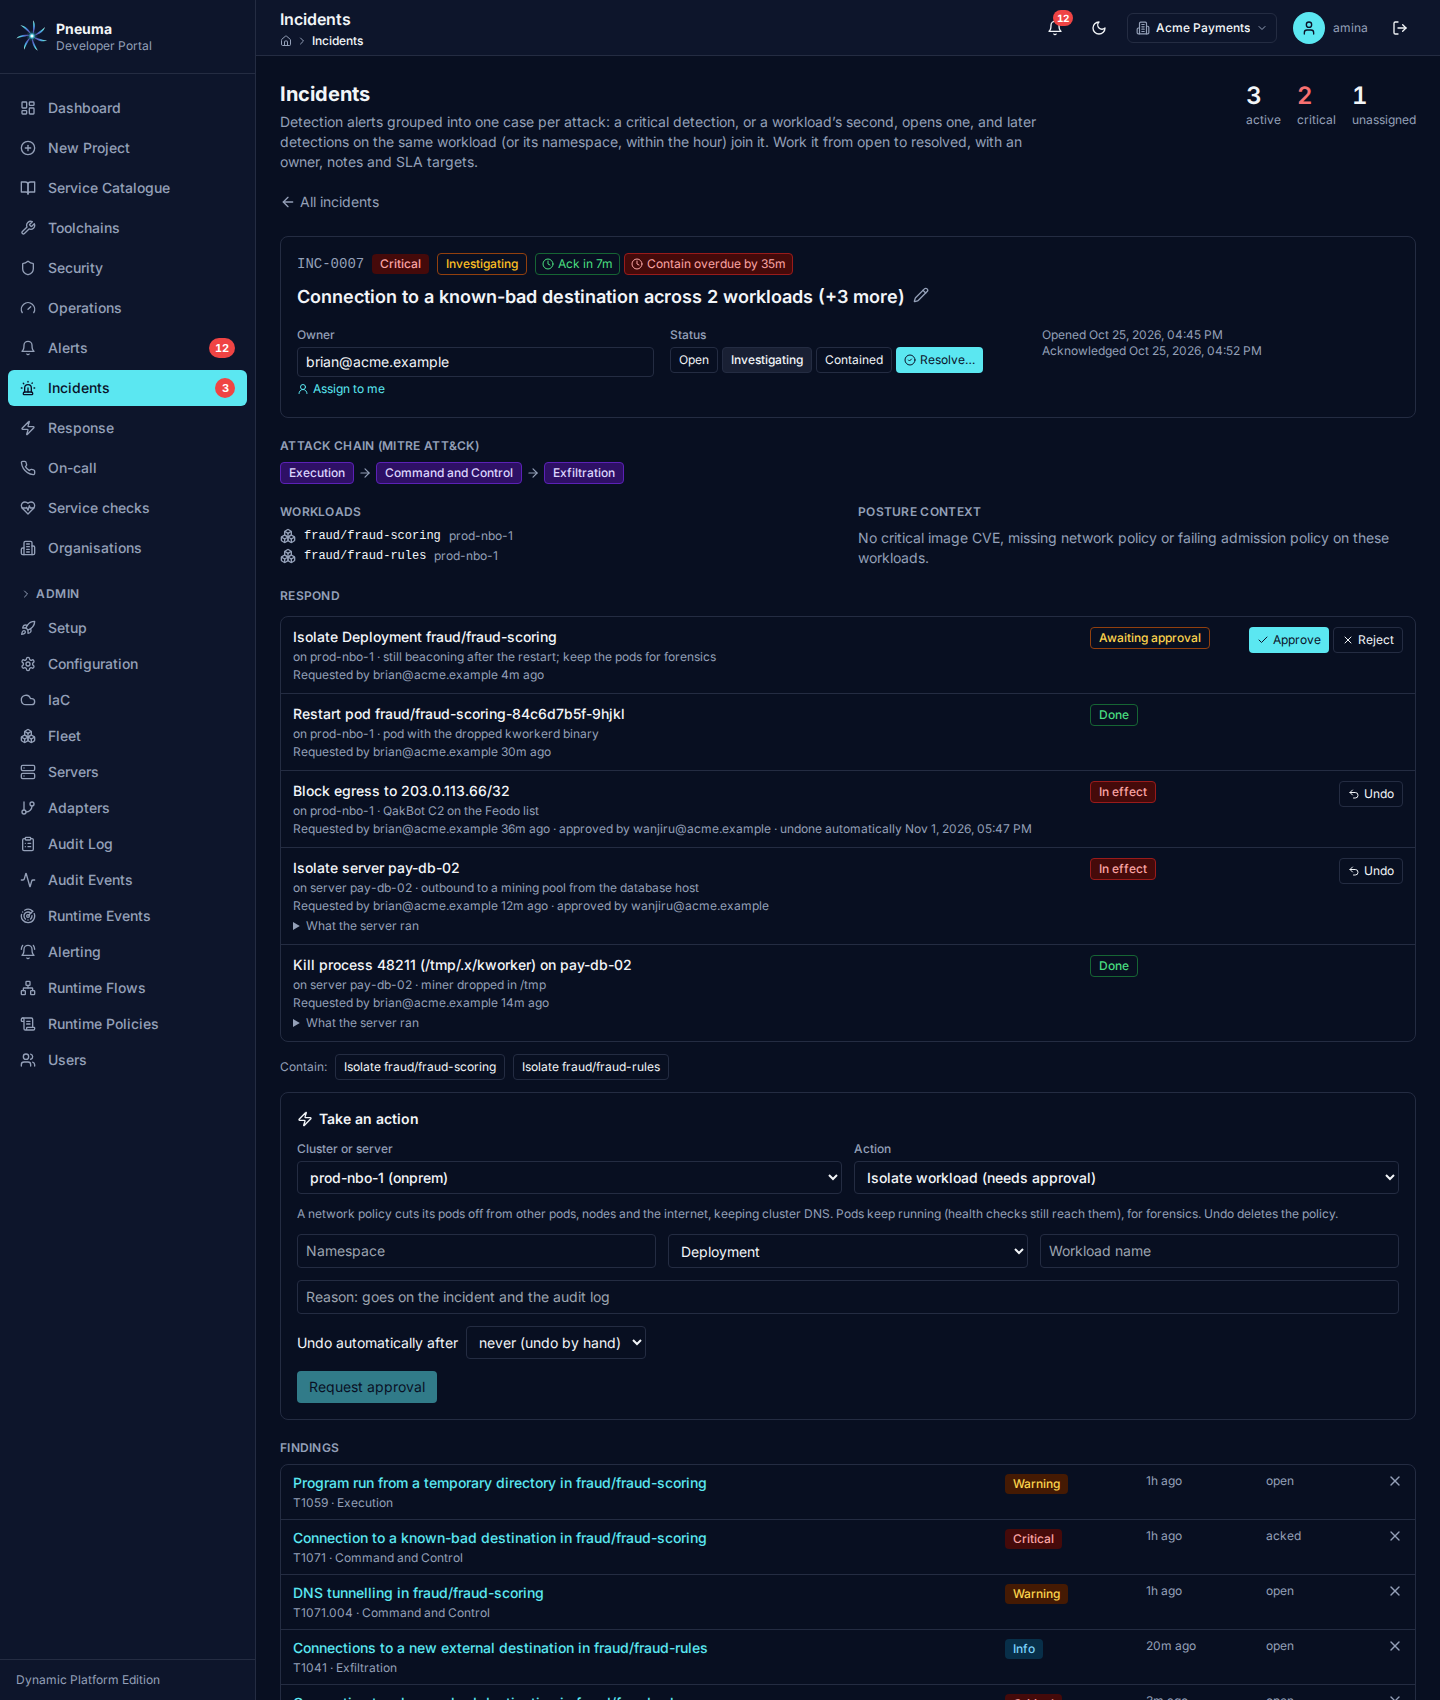
Incident detail view showing a suspected credential-stuffing incident with on-call paging timeline.
Incidents, with the timeline the auditor will ask for.
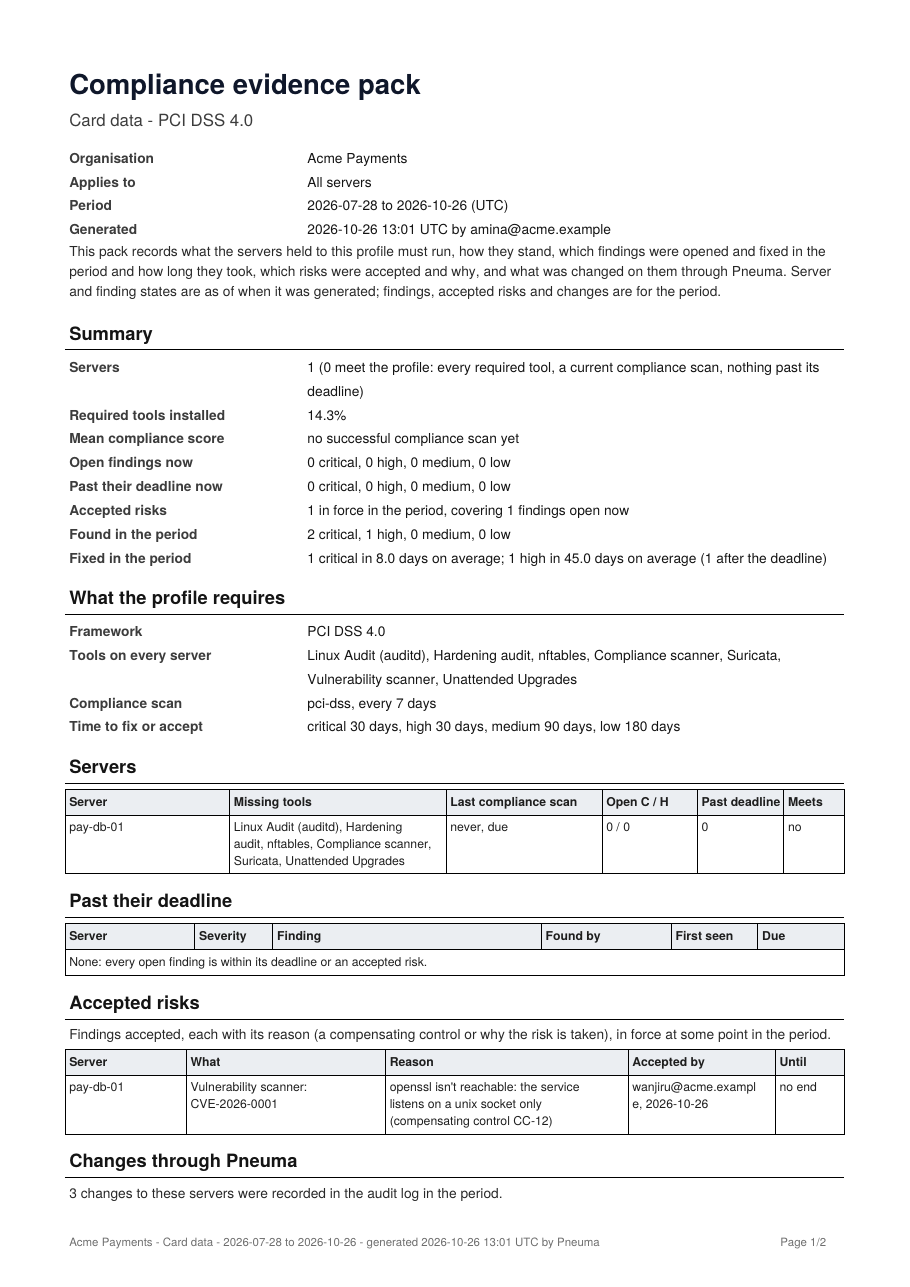
Compliance evidence pack generated as a PDF for an auditor.
One button. One PDF. The auditor's answer.
Next step

Deploy it. See what it finds.

Three months free. Signed licence. Your data stays yours. No ongoing commitment after the trial — you decide.