ISO 27001
ISO/IEC 27001
The international standard for an auditable information security management system.
Modern cybersecurity rules do not ask whether you were attacked. They ask how fast you reported, contained and evidenced it. Pneuma gives you the evidence.
Kenya shown as the illustrative example — the shape is the same across every regulated market. The attack surface is not theoretical. The losses are not hypothetical.
cyber-threat events detected in Kenya, Jan–Mar 2026
Communications Authority of Kenya
were system attacks, mostly on critical infrastructure
Communications Authority of Kenya
stolen from Kenyan bank customers in 2024 — almost 4× 2023
Central Bank of Kenya via Business Daily
lost to cybercrime in Kenya every year, at the least
Interior CS, April 2026
Typical windows across financial-services and data-protection regulators. Exact numbers vary by jurisdiction — the shape is the same everywhere.
Systemically-important payment systems — significant incidents must be reported.
Other payment service providers — significant incidents.
Personal-data breach reported to the Commissioner.
Notice before outsourcing, cloud included (payment providers).
These come up on almost every engagement. If your regulator or customer requires something else — SOC 2, GDPR, DORA, PDPA — the same approach applies. Reach out and we'll scope it.
The international standard for an auditable information security management system.
Mandatory controls for organisations that store, process or transmit cardholder data.
US health-data protection rules that apply wherever protected health information is processed.
Consensus configuration baselines for Kubernetes, cloud accounts, Linux and container runtimes.
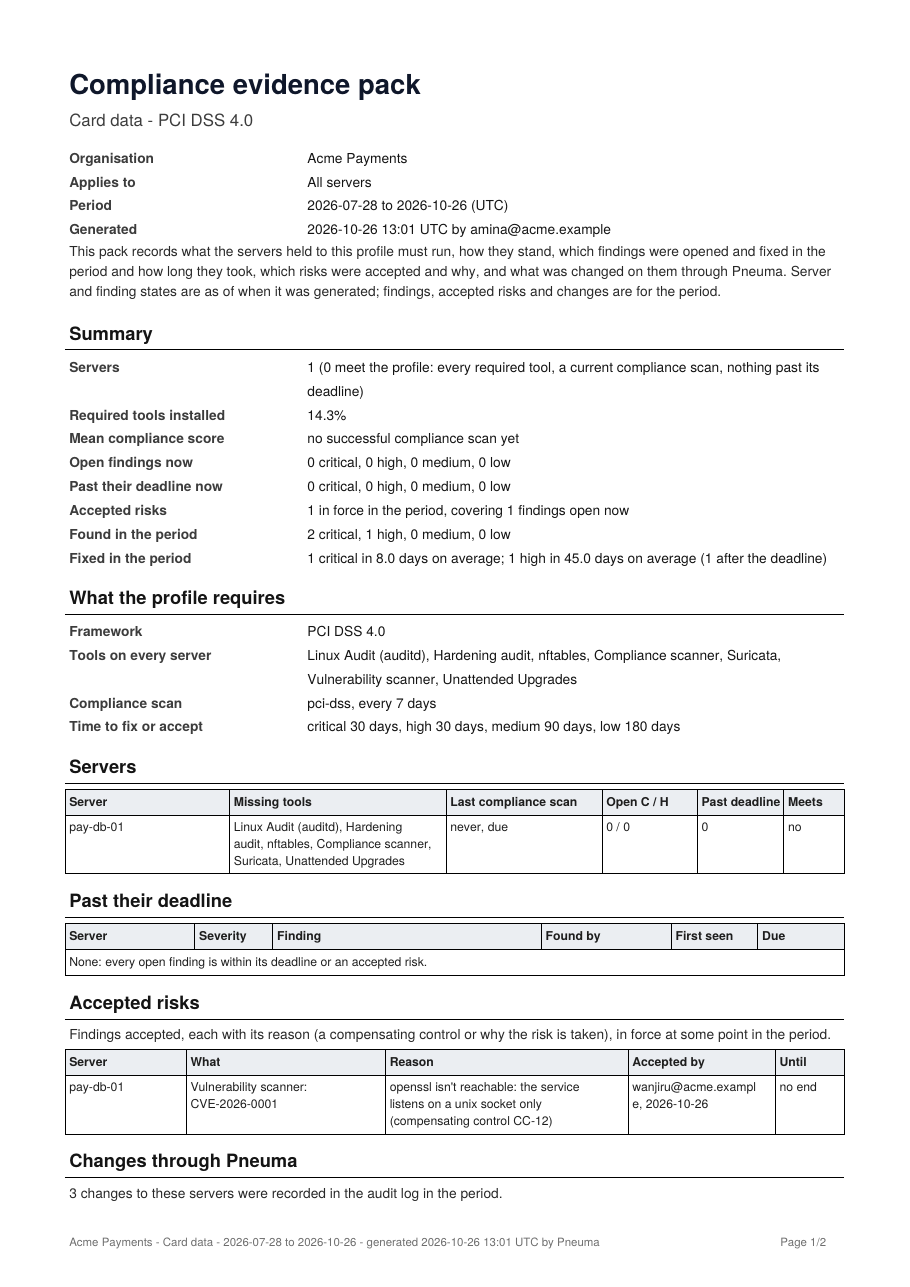
Inside the pack: what the profile requires, findings found and fixed with a CSV, findings past their deadline, accepted risks with reasons, and every change made through Pneuma plus approved manual ones.
Book a free security and compliance assessment against the regulations and standards that apply to you.
Book an assessment →